
The Dunetrails Secure Workspace Brief
Practical insights on Microsoft 365 security, NIS2 and CyberFundamentals. Readable for management and IT. Without sales talk.
One issue every week. No tool pitches, no doom scenarios.
Scan your email domain
Five minutes, free, and you know whether someone can impersonate your company by email. The scan looks at SPF, DKIM and DMARC: the three rules that decide whether fake emails bearing your name reach your customers.
NIS2 in practice
We guide SMEs through their NIS2 trajectory. In these issues we share what we learned along the way.
NIS2 is for SMEs no longer theory
What NIS2 and CyberFundamentals ask of an SME, without legal language.
We do security already?
"We do security already?" The question every audit starts with, and what it is really about.
No tickets is not the same as good management
Silence in the ticket list feels like control. Rarely is it.
What if your IT partner does not welcome an audit?
What if your IT partner does not welcome an audit? About trust and evidence.
Microsoft Secure Score & Exposure Score
Improving starts with honest measuring. Two scores that show where your environment really stands.
Email Security: SPF, DKIM & DMARC
The three DNS rules every audit checks, and that many domains still miss.
Attack Paths in Microsoft Defender
How an attacker strolls from an ordinary mailbox to global admin rights.
Is Microsoft 365 not secure enough?
Microsoft secures the platform, not your settings. That difference is exactly what NIS2 is about.
What we do
Security audit
We look at your Microsoft 365 environment the way an attacker would: identity, email, endpoints, the things that actually go wrong. You get an honest picture of where you stand, in plain language.
More about the auditManaged security
The audit shows the gaps, our managed service closes them. A security overlay on your existing IT, not outsourcing: your team stays the owner, we make sure the lines stay closed.
More about our servicesMost read
The four most-read articles. Practical guides on Microsoft 365 and Defender, for anyone who has to combine security with everything else.
The mini-audit
Five questions every audit of ours opens with. You can already answer them today, in your own environment. The more honest your answer, the more you get out of it.
Is MFA enough?
MFA stops most sign-in attempts, but not all. Attackers these days hijack the session that comes after sign-in: you neatly log in with two steps, they walk along via your token. The wall is still there, the gate was simply open.
Check you can do today: see whether sessions at unusual locations or devices get terminated, and whether a policy exists that revokes tokens at risk.
Read the full issue: MFA is not a wall
Is my domain open to email spoofing?
If there is no DMARC record, anyone can send an email that looks like it comes from your company. The spoofing happens at the recipient, not with you, so your own security never notices.
Check you can do today: type your domain into mxtoolbox.com and look at the SPF and DMARC rules. Or run our free email scan right away: five minutes, explained in plain language.
Read the full issue: Email Security: SPF, DKIM & DMARC
Does my SME need to think about NIS2?
For many SMEs NIS2 is no longer theory, also for those not formally obliged: customers and insurers ask more and more often. CyberFundamentals offers a workable framework, even without a legal team.
Check you can do today: ask your IT lead about the last baseline measurement. If there is none, that is the honest starting point.
Read the full issue: NIS2 is for SMEs no longer theory
We get no tickets, so everything is fine?
A silent ticket list usually means nobody is looking, not that nobody is getting in. Many problems never cause a single alert.
Check you can do today: open the Microsoft 365 admin center and look at users without multifactor authentication. That overview is wrong more often than people think.
Read the full issue: No tickets is not the same as good management
Where is the best place to start?
With a baseline measurement. Not with a tool, not with a project plan: first know where you stand, then set priorities. That is how every audit of ours starts too.
Check you can do today: book a half-hour conversation. We look together at where you stand today.
Read the full issue: From zero measurement to a secure workplace: a step-by-step plan
All issues
Every issue of the Brief, newest first. RSS feed
Why local admin rights are expensive
The largest crypto heist ever started with one download nobody had approved. What local admin rights, app curation and Intune have to do with it.
MFA is not a wall: how hackers hijack your session tokens
How do hackers hijack Microsoft 365 session tokens and bypass MFA? Learn how the token spraying attack works and which 4 steps protect you right away.
Buying tools is not security
Scanners, alerts, logs: everything is on, but who is looking? On set-and-forget, false confidence and the daily follow-up rhythm that makes tools useful.
We do security already?
A year of hard work on security, and the score barely moved. Geert De Keyser (Dunetrails) on maturity, insight, and where you actually start.
No tickets is not the same as good management
An empty ticket queue is no guarantee of security. Discover why ad-hoc IT hides risks from NIS2 and audits, and how a good design prevents them.
Is Microsoft 365 not secure enough?
Microsoft 365 has strong security features, but they are not switched on automatically. What a recent tenant review uncovered, and how to set them right.
What if your IT partner does not welcome an audit?
An independent security audit assesses your Microsoft 365 environment, not your IT partner. Why partners calm down, and how to set up the conversation.
NIS2 is for SMEs no longer theory
NIS2 reaches SMEs through the supply chain, customers and insurers. What CyFun Basic asks in practice, and how to go from unknown to defensible.
From zero measurement to a secure workplace: a step-by-step plan
From baseline to a secure workplace: Secure Score, the CyberFundamentals self-assessment and tools like Maester and PingCastle, then foundation and assurance.
Identity as an Anchor: why "we have MFA" is not a security statement
Why MFA coverage is no proof of security, and why identity only works with device compliance, strong authentication and measurable controls.
Email Security: SPF, DKIM & DMARC
Learn how SPF, DKIM and DMARC protect your domain against spoofing and phishing. Test your domain with our free email security scanner.
2026: Our 6 Cybersecurity Predictions
Ransomware at its most aggressive, identity security as the new battleground and AI platforms replacing tool sprawl: our 6 cybersecurity predictions for 2026.
AI for SMEs: Opportunity or Risk?
AI can transform your SME, but it also brings new security risks. Lessons from Annacon on what you should and should not do with AI tools.
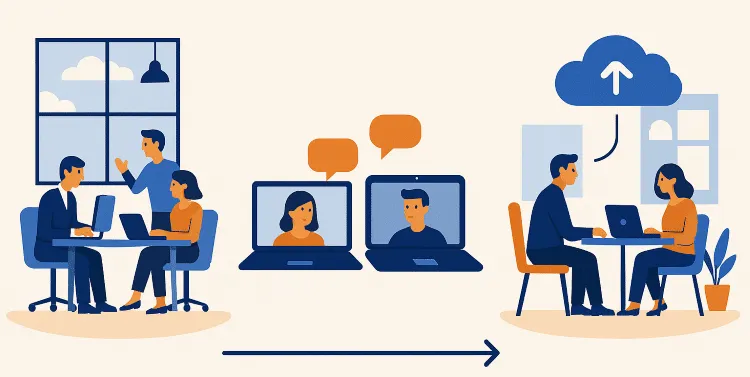
How hybrid work became the norm
Hybrid work is the norm five years after the lockdown. How technology makes the modern workplace safe and flexible for your SME.
Attack Paths in Microsoft Defender
Discover how hackers use attack paths and how Microsoft Defender, Zero Trust and Secure Score protect your network against lateral movement.
Microsoft Secure Score & Exposure Score
What do Microsoft Secure Score and Exposure Score say about your SME's security? Average scores, target levels, and how to improve both in a targeted way.
AI: a Double-Edged Sword for Cybersecurity
AI in cybersecurity: a blessing and a curse. Discover how cybercriminals use AI for deepfakes and phishing, and how your SME can deploy AI as a smart defender.
Microsoft 365 licences for SMEs: are you paying too much?
Business Standard, Premium, E3 or F3? Which Microsoft 365 licence fits your SME, what they really cost, and where SMEs overpay.
AI in Every Corner of the IT Landscape
The Dunetrails newsletter of 26 November 2025: Microsoft 365 security, AI agents, Security Copilot, new Security Agents and passwordless working.
Ignite Special: Key Microsoft Ignite 2025 Announcements
The key Microsoft Ignite 2025 announcements for SMEs: AI in Microsoft 365, new security features in Defender, Entra, Intune and Purview.
Passwordless working: can your SME start today?
Passwordless working can start today: Windows Hello and passkeys are usually already in your current Microsoft 365 licences. What you need and where to start.
The Resilience Test
Are cloud platforms really indestructible? The recent Microsoft and AWS outages raise questions. Discover how to strengthen your SME's resilience.
The Big Brother
Issue #3 of the Dunetrails Brief: AI is everywhere, from the keynotes at Annacon to what it means for your SME's workplace.
The Silent Upgrade
The silent upgrade: hotpatching in Windows 11, ransomware disrupted via Teams and changes to subscription billing. Issue #2 of the Dunetrails Brief.
Dunetrails Secure Workspace Brief #1
Issue #1 of the Dunetrails Secure Workspace Brief: Windows 10 End-of-Life, NIS2 compliance and the latest AI security features for SMEs.
Written by Geert
I have worked in IT for more than 25 years, these days as a security specialist and auditor. The things in the Brief are what I see during audits at real organisations: the MFA gaps, the forgotten admin accounts, the DNS records nobody ever checked. I write them down so you do not have to experience them yourself.
Every week in your inbox
One issue every week. No tool pitches, no doom scenarios. And if it gives you nothing, the unsubscribe button works just as well as the subscribe button.
Want to know how your environment is doing?
Every Brief starts somewhere, at a real environment. Yours could be next.